

 EN
Announcing the Sealer2100 Bounty: Putting 10 BTC on the Line Before You Trust It
 Security Department2026/5/26
Most hardware wallets ask you to take their security on faith. Read the spec sheet. Look at the certifications. Trust the manufacturer. The Sealer2100 bounty program takes a different position: try to break it, and if you're first to succeed, keep the prize.
That's not a marketing angle. It's a formal, structured challenge with real stakes. The 10 BTC Growth Fund is open to researchers and bounty hunters who can find and responsibly disclose a verified vulnerability.
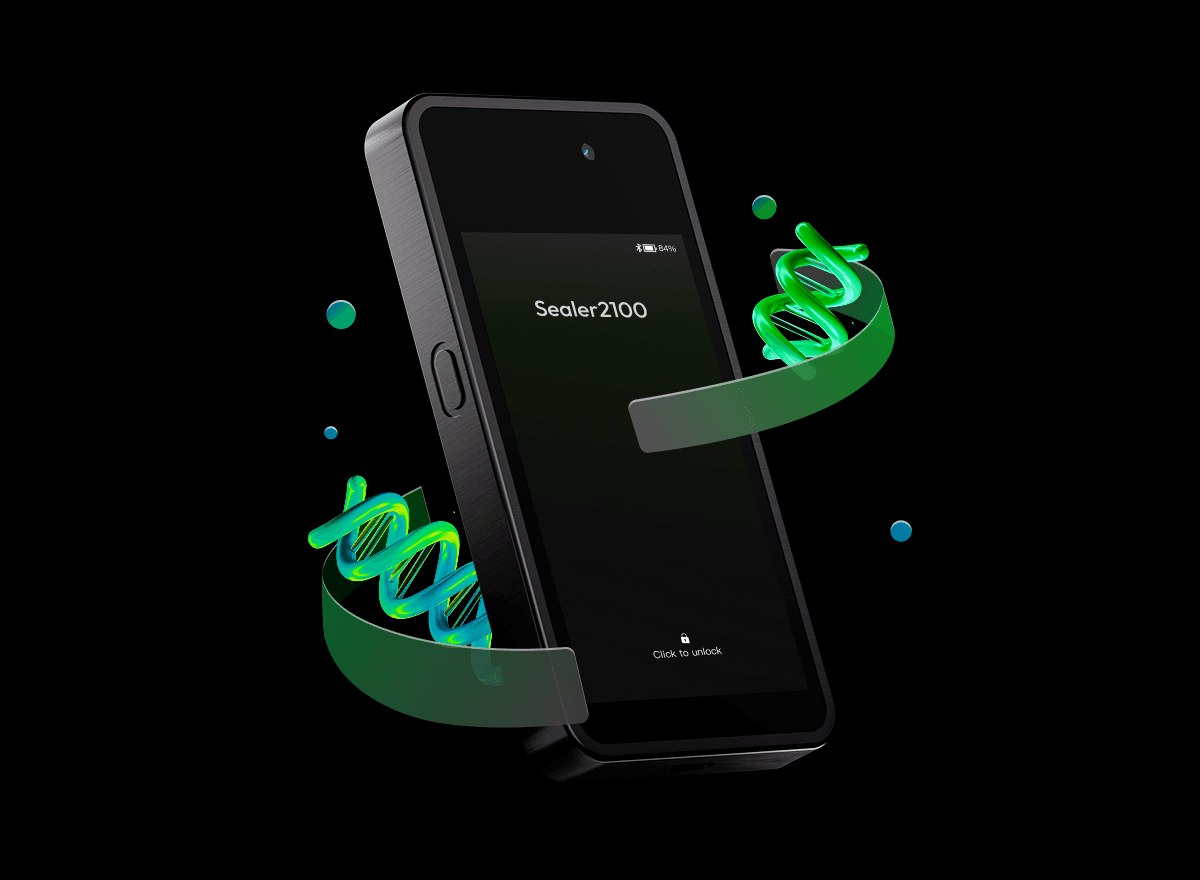
The White Hat Bounty Edition runs alongside it, limited to 100 devices available during the pre-sale opening June 18, 2026, with 1 BTC going to whichever buyer is first to breach one.
Why Security Claims Aren't Enough Anymore
The numbers from 2024 are not subtle. According to Chainalysis, hackers stole approximately $2.2 billion in cryptocurrency that year, a 21% increase over 2023. The number of individual hacking incidents rose 7.4% over the same period.
More striking is how most of that money disappeared: private key compromises alone accounted for 43.8% of all stolen crypto in 2024. That's the single largest attack vector, and it's precisely the weak point that hardware wallets are supposed to address.
The pattern behind these thefts matters too. North Korean state-affiliated hackers stole an estimated $1.34 billion across 47 incidents in 2024, representing 61% of all cryptocurrency stolen that year.
These groups don't just rely on brute force. They use social engineering, infiltrate companies, and increasingly target centralized exchanges, which suffered more than $726 million in losses in 2024 according to Immunefi. The threat isn't coming from opportunistic actors working alone, but also from organized, well-funded operations that keep adapting.
Against that backdrop, asking users to simply trust that a hardware wallet is secure feels inadequate. Words are cheap. Even certifications, while meaningful, describe a snapshot of security at a point in time, tested under controlled conditions. What actually tells you a product holds up is whether it survives real adversarial pressure from people actively trying to make it fail.
What the Sealer2100 Bounty Program Actually Is
The 10 BTC Security Season is structured around two tracks that serve different audiences: one for security researchers, and one for buyers willing to run their own test.
The Growth Fund bounty program allocates a pool of 10 BTC for security researchers who identify and responsibly disclose verified vulnerabilities in the Sealer2100. Researchers who find genuine weaknesses are rewarded from that pool. This format has proven effective at surfacing real vulnerabilities across the industry.
Immunefi, the blockchain security platform, surpassed $100 million in payouts to ethical hackers from over 3,000 bug bounty reports, and has documented saving more than $25 billion in user funds across Web3 protocols. When the prize is large enough relative to the effort, capable researchers look seriously.
The White Hat Bounty Edition is a different kind of test entirely. One hundred limited edition units of the Sealer2100 are offered at $899 each. Every device in that batch comes pre-loaded with 21,000,000 Sealer tokens. The mechanic is straightforward: the first person across all 100 devices to successfully breach the hardware's security and access those tokens wins 1 BTC. One prize. One winner. The race is open to all 100 buyers simultaneously.
That distinction is worth sitting with. This isn't 100 separate individual challenges running in parallel. It's a single competitive test with a pool of 100 motivated adversaries, each holding a live device and each aware that someone else may find the exploit first. That pressure changes how seriously people look.
And it means the security holds, or it doesn't, against a concentrated wave of real-world attempts happening at the same time.
Why Open Challenges Say More Than Closed Audits
There's a meaningful difference between a company conducting its own security audits, hiring external penetration testers, and openly inviting anyone in the world to try and break the product for money.
Closed audits are valuable, but they have limits. The scope is defined in advance. The testers are known and vetted. The timeline is fixed. Genuinely creative attacks, the kind that come from someone who has spent months thinking about one specific attack vector, rarely emerge from structured engagements with preset deliverables.
Open bounty programs change the economics. 1Password raised its maximum bug bounty reward to $1 million in 2022. After nearly 800 attempts from researchers, all detected bugs were classified as minor and posed no threat to sensitive customer data. The scale of participation that meaningful rewards attract is exactly the point: you want as many capable people as possible looking for weaknesses, not a small team working under contract for a fixed number of weeks.
The Sealer2100 bounty operates on the same principle. The White Hat Edition adds a layer that most bounty programs don't have: a physical, funded device in the hands of someone who paid for it and knows exactly what's at stake if they get there first.
What the Device Is Actually Defending Against
To understand what you're testing, you need to know what the Sealer2100 is built around.
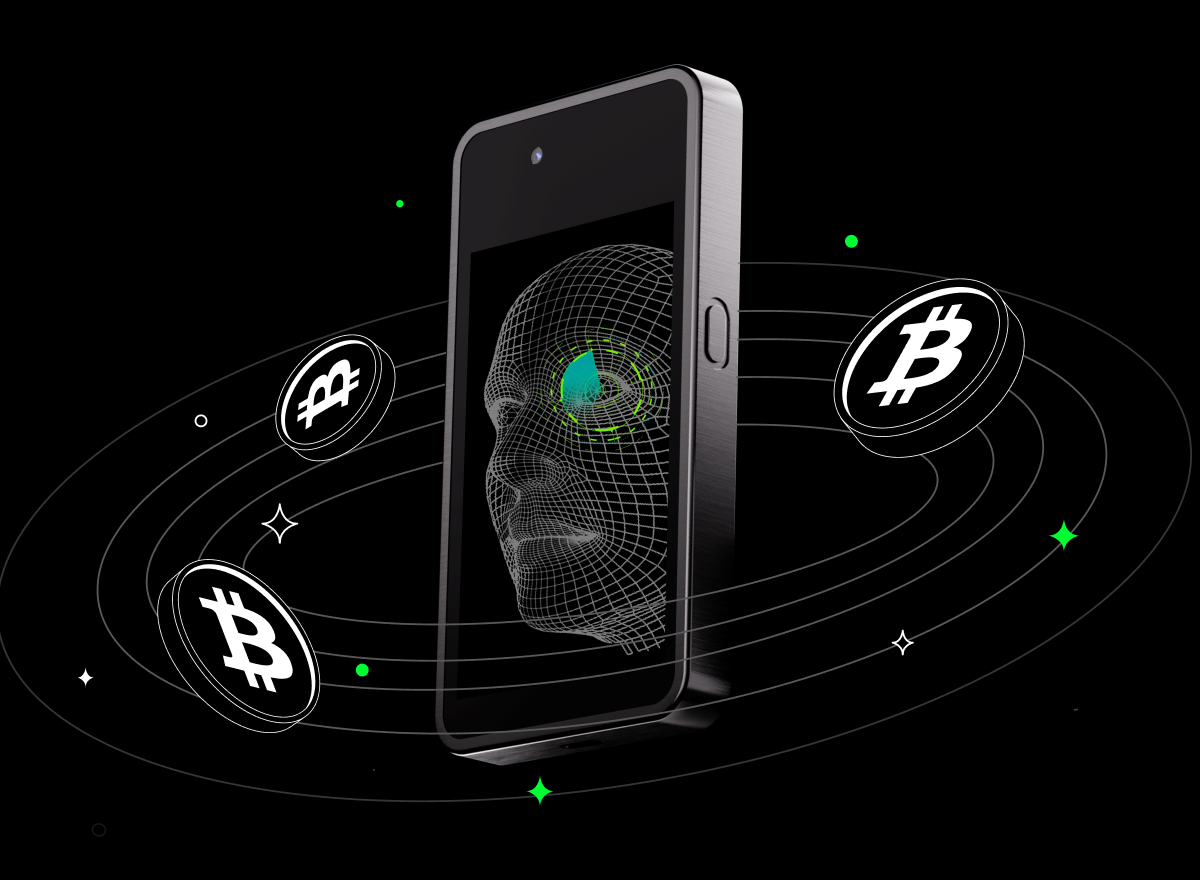
The device stores private keys in a CC EAL6+ certified TMC THD89 secure element, physically isolated from the main processor. Iris templates are encrypted and stored within that same chip, with no network transmission pathway. The iris recognition system uses 2048 encrypted biometric feature points with infrared liveness detection, designed to counter spoofing attempts using photographs, silicone replicas, or 3D-printed models.
Transaction signing happens offline via AirGap QR code, meaning the private key never touches an internet-connected device during the signing process. Compatible with 12 major wallets including MetaMask, OKX, and iToken, the workflow generates a transaction QR code on the connected app, signs it offline on the device, then exports the signed transaction QR back to the app. At no point does the key travel across a wireless or wired connection.
The physical body is titanium alloy with high-transparency reinforced glass. The device runs a 3.5-inch MIPI full-lamination display at 480×800, weighs 130g, and supports approximately 100 minutes of continuous signing on an 800mAh battery. These aren't just spec-sheet details. They're the surface the White Hat Bounty challengers will be working against: hardware-level isolation, biometric verification, and zero-contact transaction signing all in a single physical form factor.
Who Should Pay Attention to the Sealer2100 Bounty
Security researchers are the natural audience for the Growth Fund. If you can find a real vulnerability in a hardware wallet claiming CC EAL6+ certification and iris-based biometric security, 10 BTC is a serious reward pool that warrants serious attention.
The challenge is designed to draw people who already work in hardware security, cryptographic implementation review, or biometric systems analysis.
For everyone else, the White Hat Bounty Edition raises a different question. Most people buying a hardware wallet are not going to personally audit the firmware. They're trusting that others have.
The 100 White Hat Edition devices create exactly that process at scale: 100 buyers, each holding a live device, collectively competing to be the first to break what the manufacturer says can't be broken.
If any of the 100 devices is compromised, the winner claims 1 BTC and the security team has a verified exploit to work from before mass production. If none of them are, the device has passed a practical, adversarially-run test that no internal certification process can replicate. Both outcomes produce better information than a datasheet.
The pre-sale opens June 18, 2026, timed to coincide with the FIFA World Cup window. Global production is capped at 2,100 units total.
What a Bounty Program Tells You That Specifications Don't
Specifications describe what a product is supposed to do. A bounty program tells you whether it actually does it when someone is actively trying to make it fail.
The 2024 crypto theft data makes the case plainly. Private key compromise was the leading cause of stolen crypto. Centralized exchanges, despite significant security investment, kept getting hit. The threat landscape does not reward complacency, and it doesn't reward trusting vendor claims that haven't been pressure-tested.
Open bug bounty programs in blockchain and Web3 paid out more than $65 million for discovered vulnerabilities in 2023 alone. That scale of payout reflects a shared industry understanding: adversarial testing finds what internal review misses.
The Sealer2100 bounty joins that ecosystem with a specific, time-bound, high-stakes challenge that goes further than most by putting physical funded devices directly in the hands of challengers.
Whether you're a researcher with the skills to probe a hardware-level exploit, or a potential buyer who wants to know what 100 motivated adversaries found when they tried, the results of this challenge will be more informative than any certification document.
Security that hasn't been seriously challenged is a hypothesis. Security that has survived a competitive, real-world test is closer to a fact.
White-Hat First: Why We Invited Hackers Before Shipping Sealer2100
 5/26